 binfera
See what a binary does.
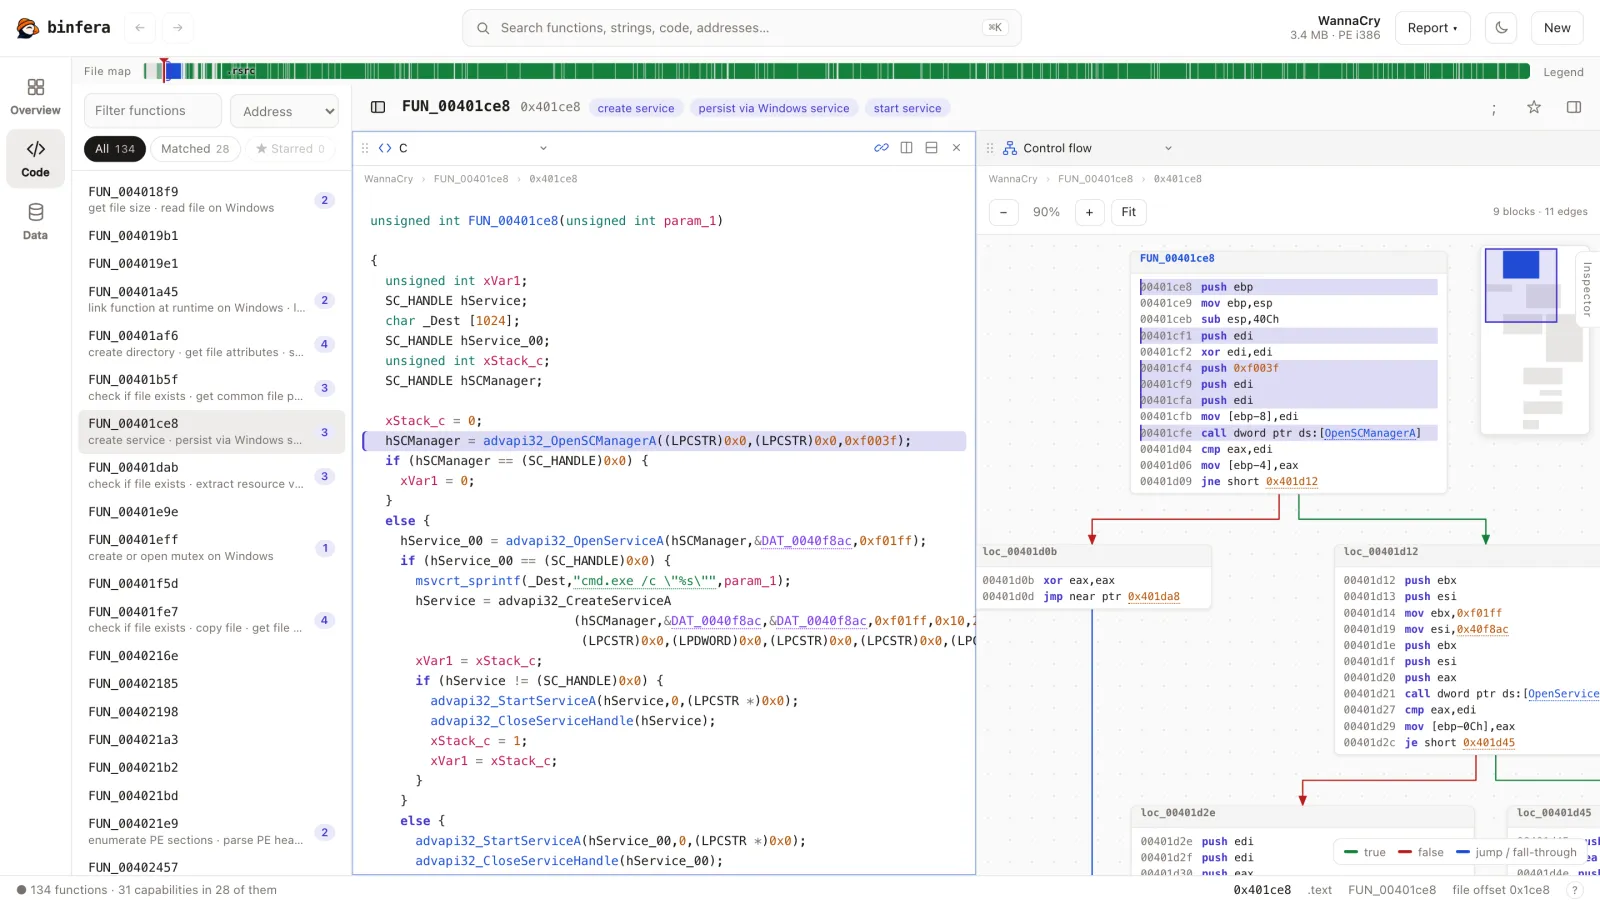
Decompiled C, capabilities and diffs for Windows, Linux and macOS executables, right in your browser.
- Results stay in this browser. Nothing uploaded.
- No install
- No account
No file? Try a harmless demo.
A small program bundled with Binfera.
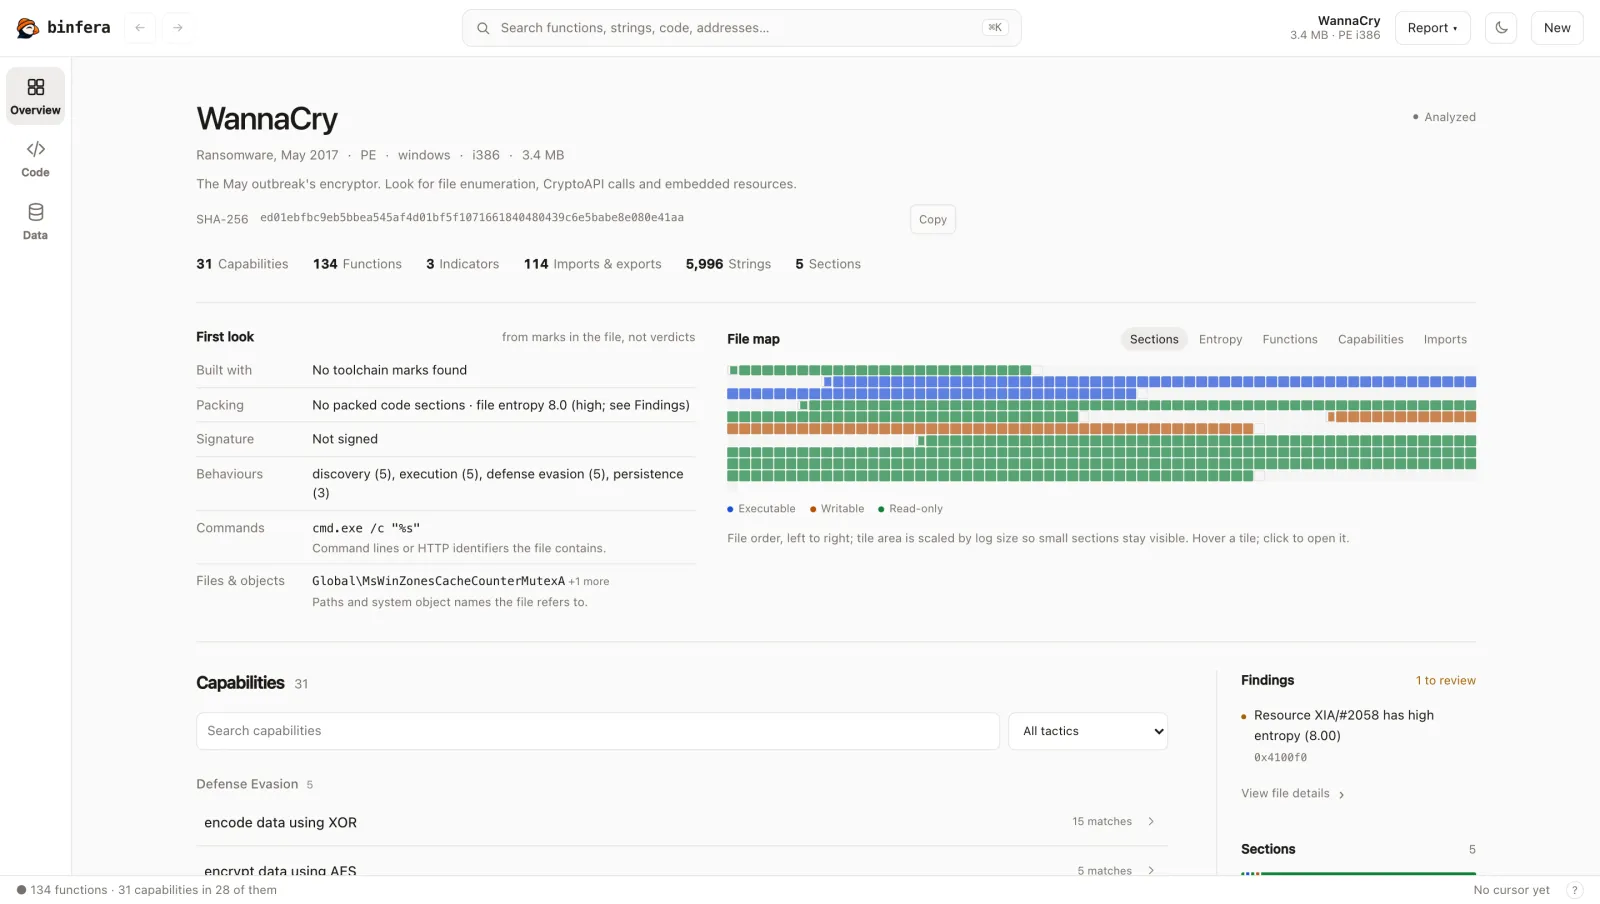
Built for the first hours with an unknown file
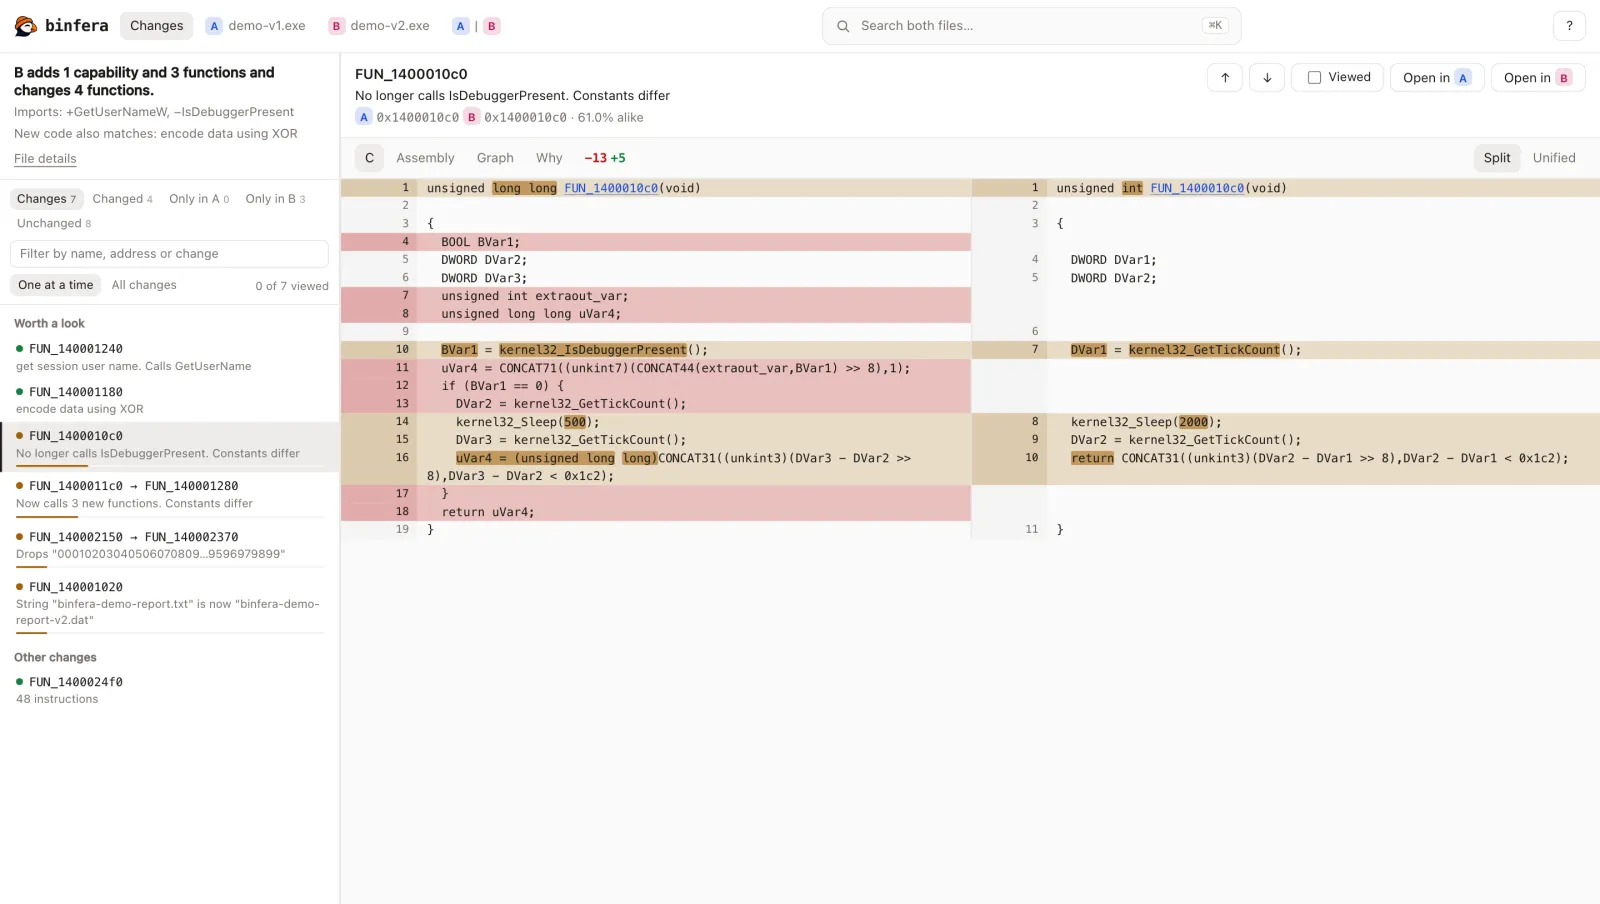
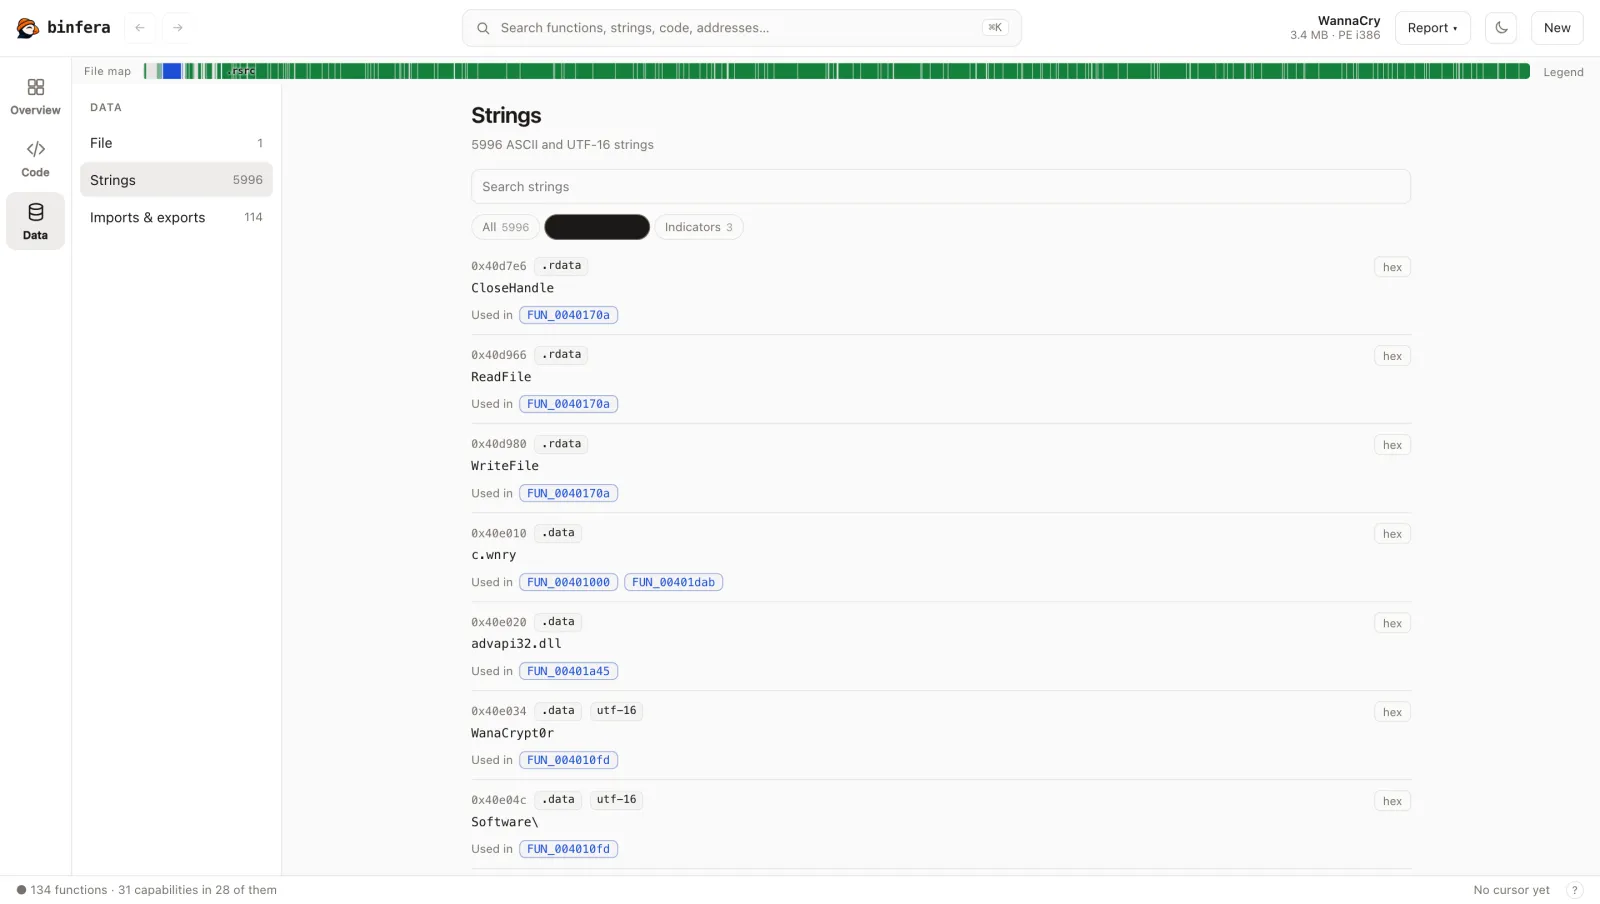
What is it, what does it do, and what changed.
Whatever you're handed
PE, ELF, Mach-O or raw shellcode, directly or inside zip and 7z. x86, x64, AArch64, ARM32 and MIPS32.
Library code named
FLIRT signatures and Function ID packs label what isn't worth reading.
Your work stays
The desktop app keeps renames, comments and recent files, and browses whole folders of samples. Download
Function emulation
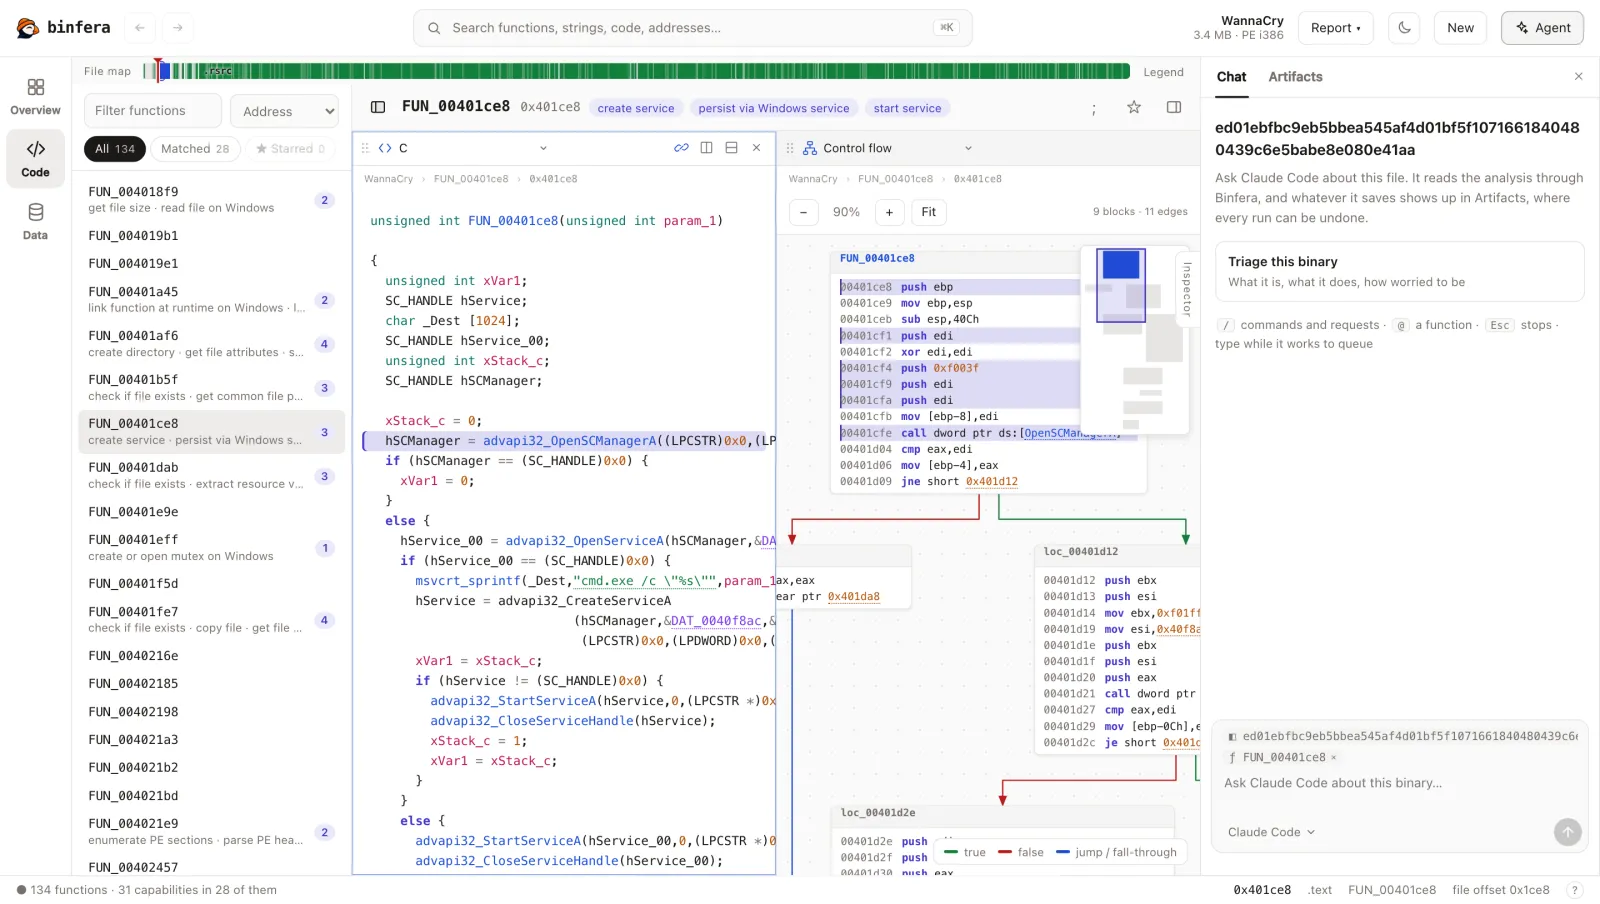
From the command line or MCP, run a function on emulated memory. Sample code never executes on your CPU.
Fast first look
A function list a median of 23 times sooner than Ghidra's headless analyzer, on PE, ELF and Mach-O files. Caveats
Scripts and CI
binfera diff checks builds in a pipeline, and Python bindings expose inspection and decompilation.